Technical & Security Audit

Know exactly where your technology stands, and what to do next.

Inherited a codebase, running old software, planning to scale or facing due diligence? We review your code, architecture, security and delivery process independently, then give you a ranked plan you can act on, and help you fix it.

Products we’ve taken over and improved

products built and scaled, GeekyBones
100+
products built and scaled
long-term client relationships, GeekyBones
90%
long-term client relationships
years of engineering experience, GeekyBones
10+
years of engineering experience
Who it's for

Teams inheriting a codebase, preparing for investment, running unsupported software, or asked about security by a customer or insurer.

The outcome

A clear, honest picture of your technology and a plan you can act on, with or without us.

Sound familiar?

When an audit makes sense

What teams tell us, and what we do about it.

  • 01

    We inherited a codebase and don’t know what’s in it.

    How we help

    We map the system, document how it works and flag what’s fragile before anyone changes it.

  • 02

    Our developers say it needs a rewrite. Does it?

    How we help

    An independent view: what to keep, what to fix and what is genuinely worth rebuilding.

  • 03

    Investors or buyers will review our technology.

    How we help

    Technical due diligence with a plain-language report on risks, security and scalability.

  • 04

    Releases are slow and keep breaking things.

    How we help

    We review testing, deployment and process, and show where the delays actually come from.

  • 05

    A new vulnerability was announced and we don’t know if we are affected.

    How we help

    We check the versions, settings and exposure of every server and app in scope, and tell you what to patch first.

  • 06

    We run software that is old or no longer supported.

    How we help

    We map the risk, put stop-gap protection in place and plan the safest route to a supported version.

  • 07

    We need a second opinion on our architecture.

    How we help

    Hands-on consulting from engineers who have built and scaled similar products.

  • 08

    We think we may already have been hacked.

    How we help

    We look for signs of a break-in, help you contain it and close the way in.

Talk to us about your situation
What you get

A report you can act on

Findings ranked by business impact, not a list of every nitpick.

Request a consultation
  • 01

    Code review

    Quality, structure, test coverage and maintainability.

  • 02

    Architecture assessment

    How well the system will hold up as you grow.

  • 03

    Security review

    Known vulnerabilities, end-of-life software, injection and access-control flaws, server hardening, secrets and access.

  • 04

    Infrastructure review

    Hosting, deployment, backups and monitoring.

  • 05

    Delivery process

    How work moves from idea to production, and where it stalls.

  • 06

    Technical debt map

    What’s costing you most, and what can safely wait.

  • 07

    Prioritised roadmap

    Fixes in order of impact, with effort estimates, and help to patch or upgrade.

  • 08

    Executive summary

    A plain-language readout for non-technical leadership.

How it works

How an audit works

A short, fixed-scope engagement.

  1. Scope

    Agree what to review and what decisions the audit needs to support.

  2. Review

    Read the code, test the system and interview your team.

  3. Report

    Findings ranked by risk and business impact, with a roadmap.

  4. Readout and fix

    Walk your team through it. Act on it yourself, or have us patch, upgrade or harden.

Case studies

Products we’ve taken over and improved

Designed, built or rescued end to end by GeekyBones.

Mobility / Transportation

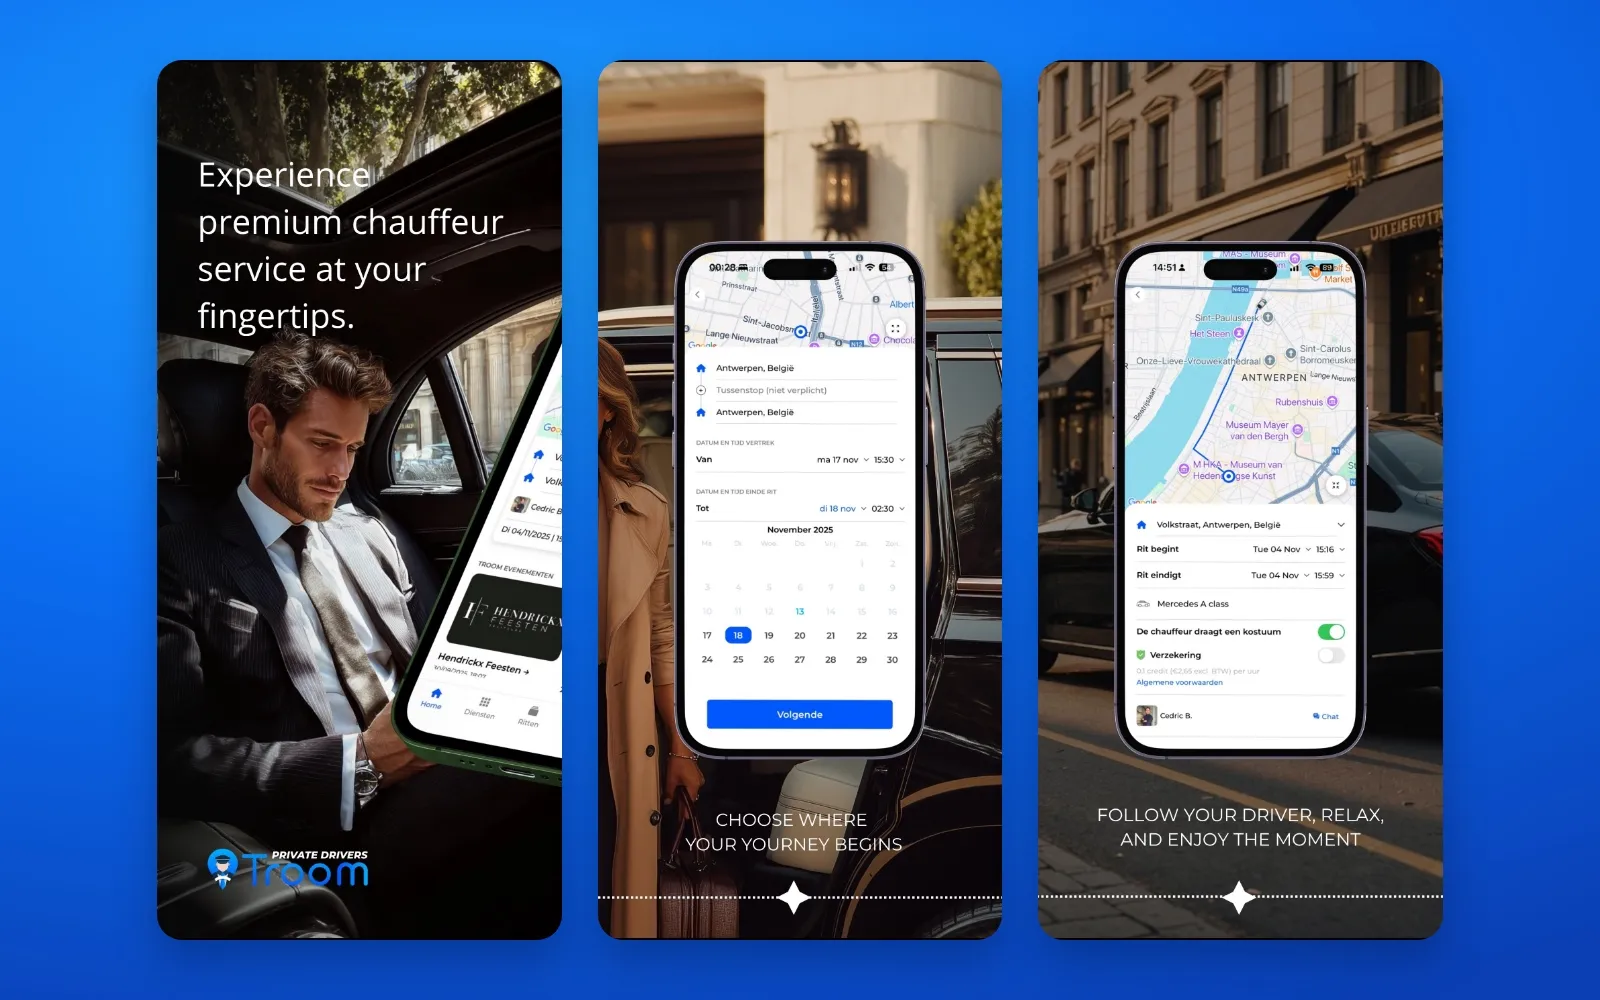
Troom – Private Driver App

Problem
People wanted to be driven in their own car, for business trips or evenings out, without parking stress or driving home themselves.
Solution
One iOS and Android app for customers and drivers, with hourly booking, nearby-driver matching and credits.
Result
Live on iOS and Android across Belgium, with 1,000+ rides every month and growing.
View case study Troom
Coverage

What we look at

The stacks and tools we see most often. If yours is not listed, we still review it: we work with any language, framework or hosting setup.

Application

  • PHP
  • Symfony
  • Laravel
  • Node.js
  • TypeScript
  • Python
  • React
  • React Native

Quality and security

  • Jest
  • Cypress
  • ESLint
  • SonarQube
  • Snyk
  • Composer
  • Playwright
  • GitHub

Servers and cloud

  • Linux
  • Nginx
  • Docker
  • Kubernetes
  • AWS
  • Google Cloud
  • Azure
  • Cloudflare

Delivery and monitoring

  • GitHub Actions
  • GitLab
  • Terraform
  • Sentry
  • Grafana
  • Datadog
  • Jenkins
  • Prometheus
FAQ

Audit questions

Straight answers to what teams ask before they start.

Still have a question?

Ask a senior engineer directly. We reply within one business day.

Ask us something else
01

How long does an audit take?

Most audits take one to three weeks depending on the size of the system and how much access we have.

02

Do we have to hire you to fix what you find?

No. The report is yours to act on with your own team, another vendor or us. If you want, we can patch, upgrade or harden for you.

03

Is this a penetration test or a certification?

No. The security part is a review of your code, configuration and setup, with a ranked list of fixes. It is not a formal certificate. If you need a certified penetration test for compliance, tell us up front and we will say what you need.

04

We run old or unsupported software. Can you help?

Yes. We check how exposed you are, put stop-gap protection in place, and plan the move to a supported version in safe steps.

05

Do you need full access to our code?

Read access to the repositories and environments in scope. We sign an NDA first.

06

Can you support due diligence for an investment or acquisition?

Yes. We produce a plain-language report on risks, scalability and security for non-technical decision makers.

07

Can you stay on as ongoing consultants?

Yes. Many clients keep us on for architecture guidance or a dedicated team after the audit.

Let's build what's next

Want an honest view of your technology and how exposed it is? Let’s review it together.

Tell us what you're building, fixing or trying to scale. We'll help you understand the next step.